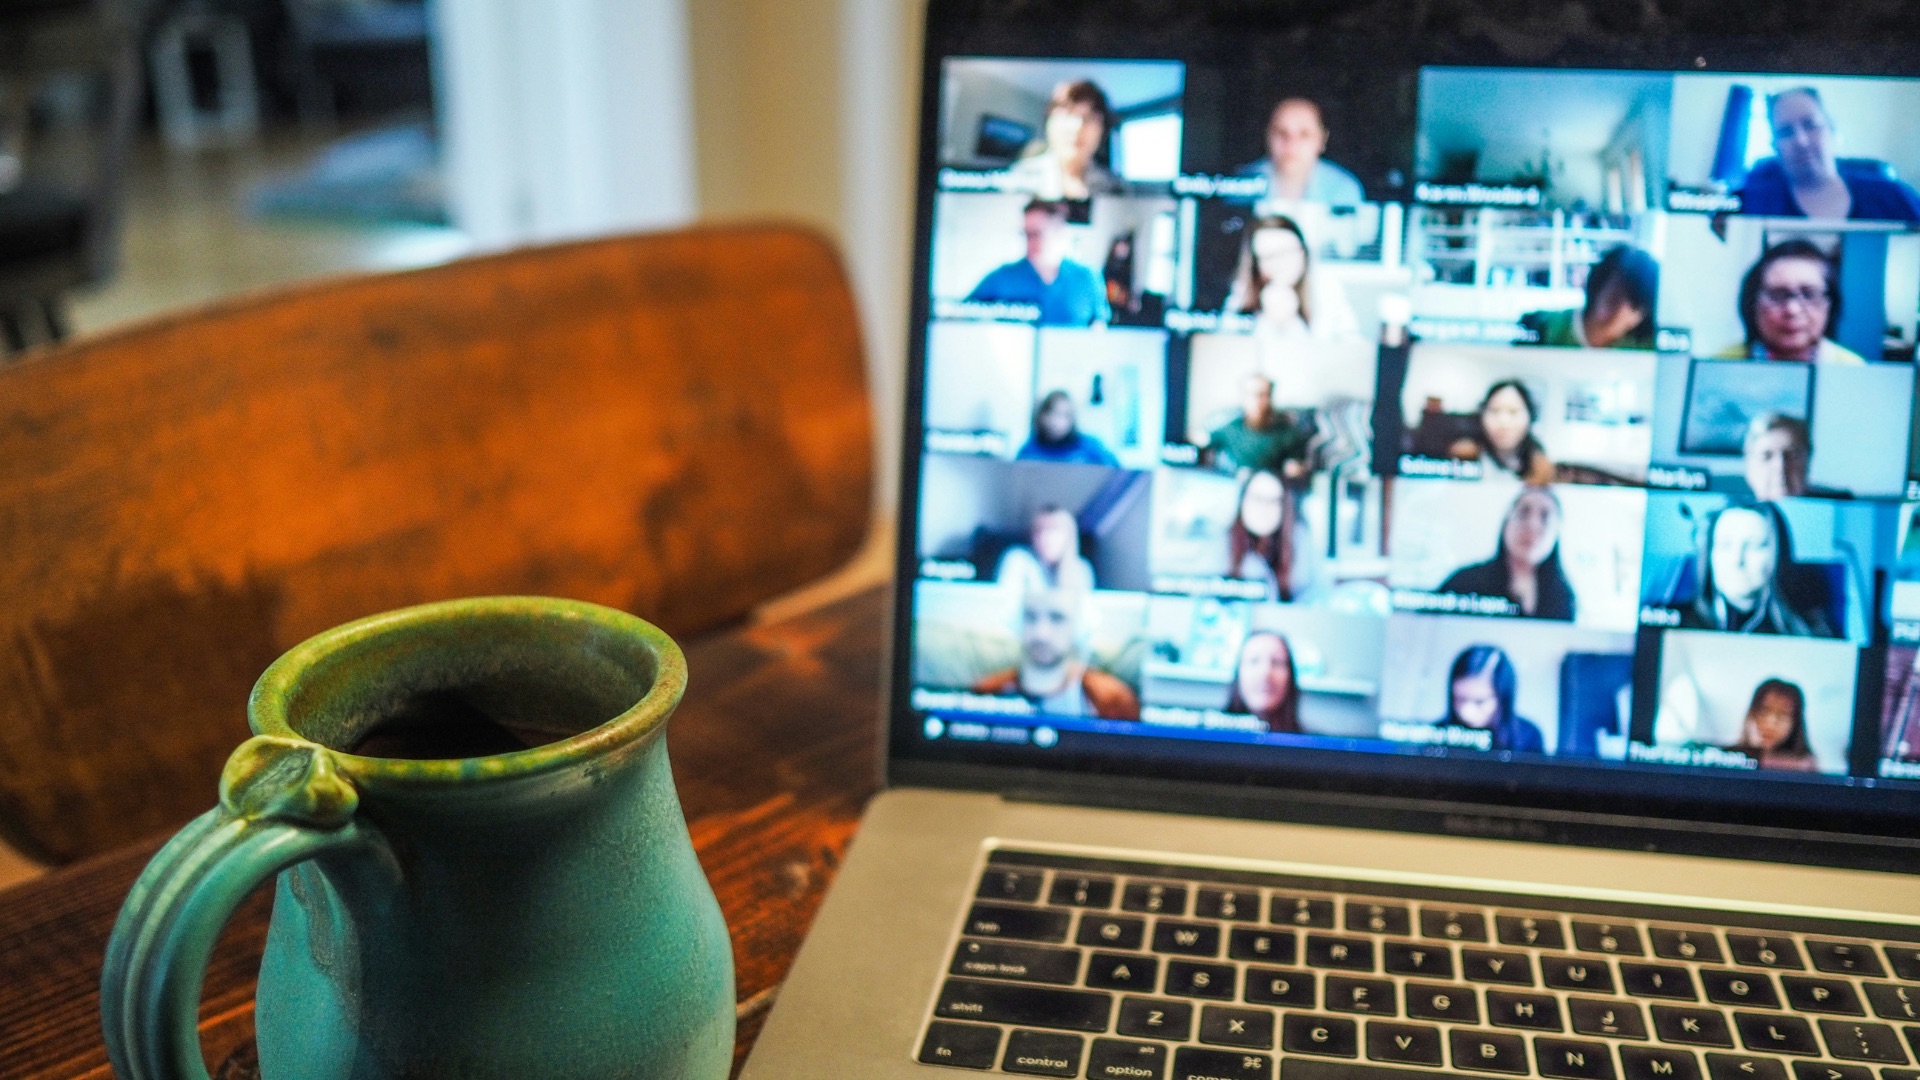
The blue glow of the monitor illuminated Sarah’s face as the clock ticked toward 2:10 PM. She was ten minutes into a high-stakes vendor call, presenting the blueprint for her company’s Q3 strategy, when a subtle pop-up interrupted her screen:
“The host has enabled an AI companion. Do you consent to data sharing?”
Sarah’s mouse hovered over the dialogue box. She had exactly three seconds to make a choice before the silence became awkward. Clicking “decline” risked booting her from the meeting entirely, bringing a critical negotiation to a grinding halt. Clicking “accept” kept the momentum going.
Like most users under pressure, she chose convenience. With a single click, the meeting resumed smoothly, but that split-second decision silently shifted her organisation’s entire risk profile without a single stakeholder’s approval.
The blind spot in procurement
Across the organisation, the IT and procurement teams took great pride in their rigorous software vetting processes. But they were fighting yesterday’s war.
The true frontier of data governance is no longer just about what software the IT team officially purchases; it is about what terms everyday users accept mid-session. As collaboration platforms silently roll out generative AI capabilities overnight, standard procurement checks fall completely short.
The company was operating under a dangerous illusion of “cloud safety,” leaning on the office consensus that because they used major, reputable software providers, data protection was the vendor’s problem.
The reality was much different. Third-party SaaS apps are a lot like a valet parking lot: the provider owns the lot, but the company still owns the car. When Sarah handed over the keys—allowing an unvetted AI model to parse a transcript packed with sensitive corporate intelligence—the provider wasn’t liable for how that model trained. The responsibility stayed entirely with her organisation.
The friction-free trap
This risk was compounded by a deeper internal issue: loose software controls. A significant number of employees in Sarah’s department operated as local administrators on their machines, making technical restrictions nearly impossible for the security team to enforce.
Without strict guardrails, local admins could easily install browser extensions or shadow SaaS tools that bypassed standard security filters. The company’s official acceptable use policy was just a static document gathering dust on the intranet. It simply couldn’t compete with the friction-free allure of a shiny new productivity tool. If users could install it to make their lives easier, they would.
The security team needed a shift in mindset. Their goal shouldn’t be to block the business from investing in tools that boost productivity; rather, security controls needed to be the very investments that enabled users to adopt new technology safely.
Key takeaways
To prevent your organisation from facing a similar mid-call dilemma, move past rigid, outdated rules and begin building dynamic, real-time guardrails:
- Empower AI consent decisions with traffic-light guidelines: Define a concrete “Red/Amber/Green” framework mapped directly to data sensitivity. Green light public and marketing discussions for AI transcriptions; amber light internal operations for vetted tools; red light sensitive corporate strategy, legal, or customer PII. This replaces 50-page intranet documents with clear, split-second decision rules for employees under pressure.
- Enforce endpoint and browser-level controls: Address risks at both levels by restricting local admin rights on the OS and applying browser management policies (such as Chrome Enterprise or Edge management). Block unapproved browser extensions, restrict unauthorised web app permissions, and prevent shadow AI extensions from bypassing standard OS security filters.
- Deploy contextual, in-the-moment guidance: Integrate Security Service Edge (SSE) or Data Loss Prevention (DLP) agents capable of triggering real-time desktop pop-ups. When a user encounters an unvetted AI prompt or attempts to share data on a third-party domain, these tools deliver an immediate prompt reminding them of the policy right when the action happens.
By replacing friction with clarity, you can ensure that the next time an AI companion knocks on the door, your employees know exactly how to answer safely.
Get in touch with our team today to discuss how we can help you.
Photo by Chris Montgomery on Unsplash
 Lucia Turner
 Iris Compañ Del Monte
 Niall McElroy
 Priya Deuchande
 Jennifer Howarth